cPANEL PLUGIN · MALWARE SCANNER · COMING SOON

Lion Exploit Scanner

Finds suspicious PHP and JavaScript code in your customers’ sites, with a quarantine that never loses a file.

A scanner built for hosting

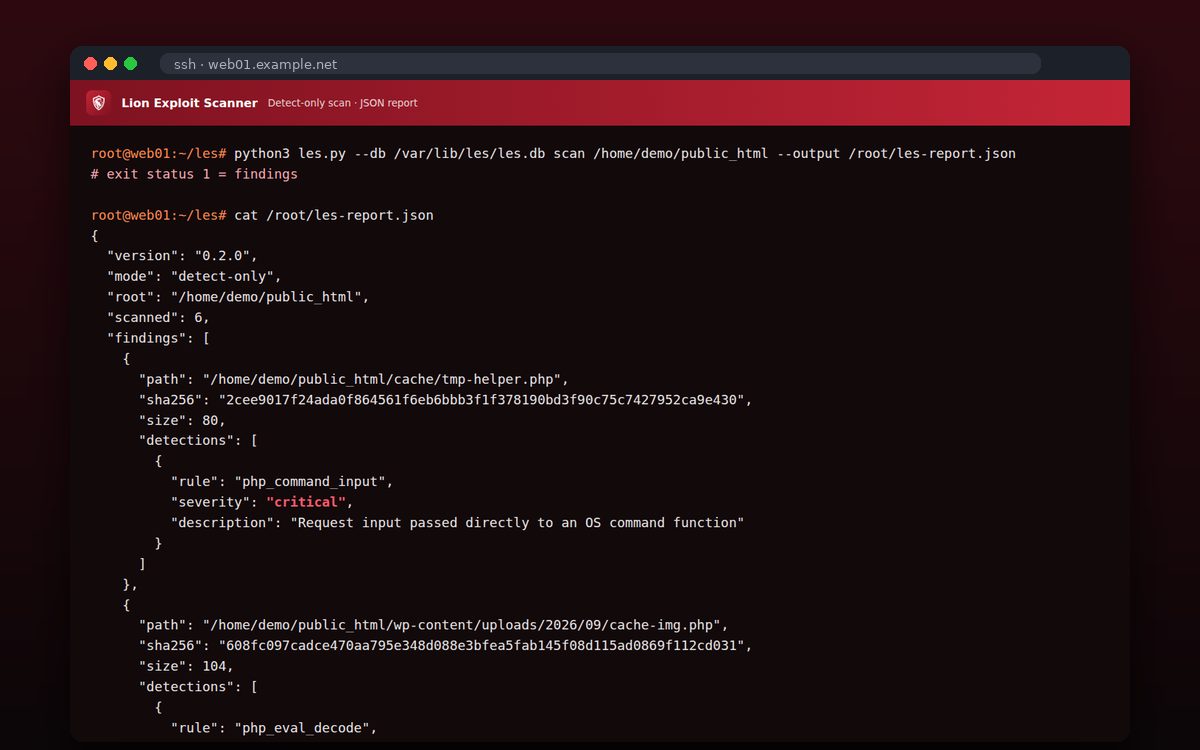
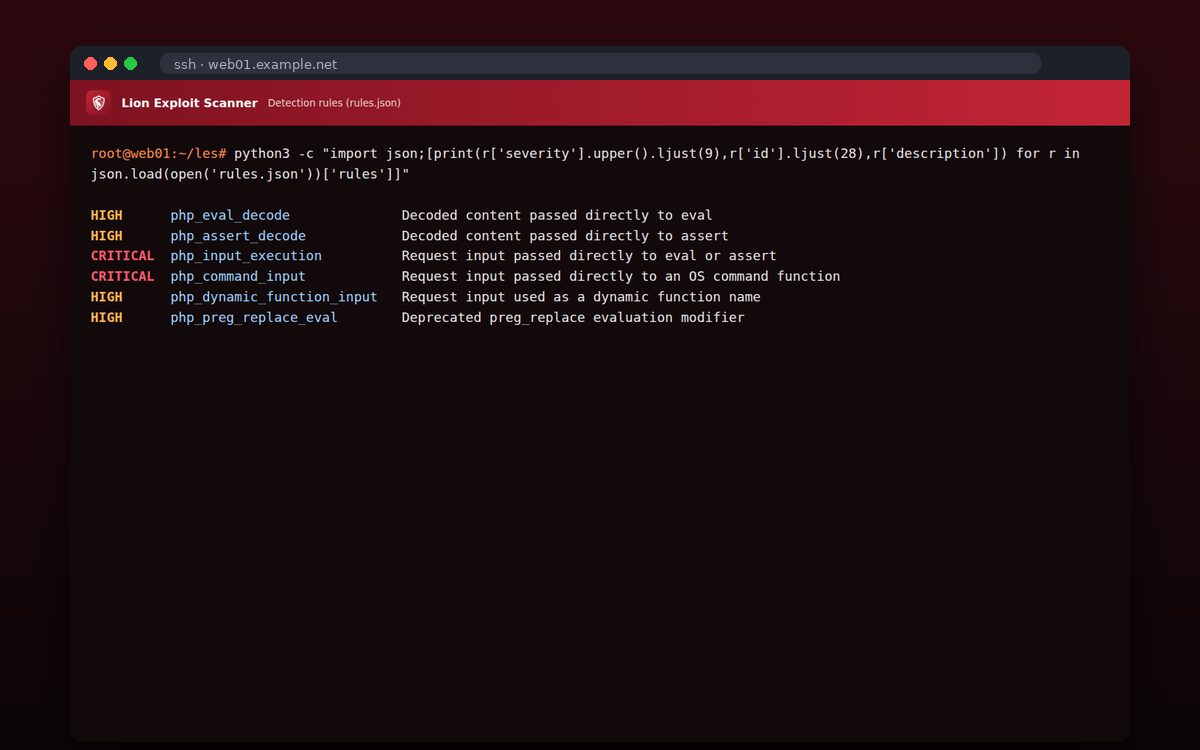
Hacked sites on shared hosting almost always leave behind PHP files that run code from the URL or decode hidden code. Lion Exploit Scanner looks for exactly those patterns: eval with decoding, system commands fed by request data, dynamic function calls and more.

It is written in Python with no external libraries, from scratch, with no code or signatures from other products. Rules live in a separate JSON file, so they can be updated without changing the program.

No automatic deletion

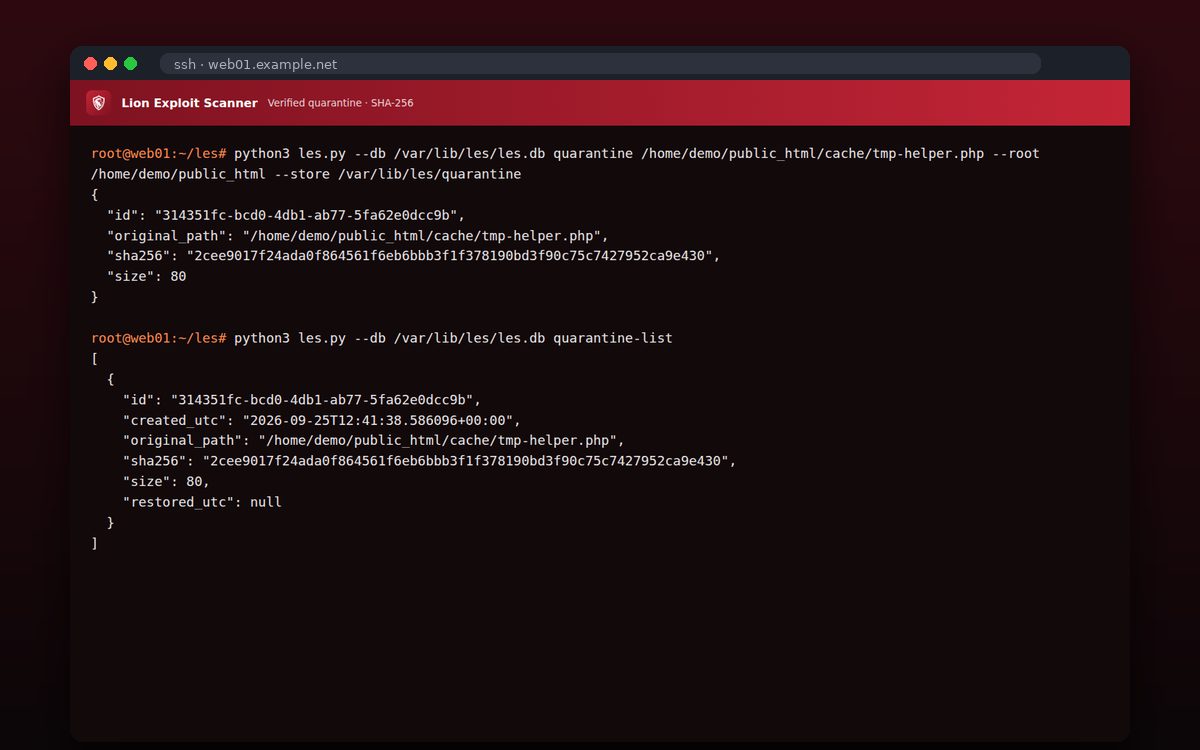
Scanning only detects. Quarantine is manual, one file at a time, after you review it: the file is copied, verified with SHA-256 and only then removed from its place. Restore never overwrites an existing file.

FEATURES

Features

🔍

Static PHP/JS analysis

Rules for eval, system commands and hidden code.

📄

JSON rules

Easy to update and extend.

🧾

Reports & history

JSON reports and scan history in SQLite.

🔒

Safe quarantine

Copy, SHA-256 verify, then remove.

♻️

Restore

Restore without overwriting existing files.

⏱️

Scheduled scans

A systemd timer for regular scans.

Who it is for

FAQ

Frequently asked questions

Does it replace an antivirus like ClamAV?

No. It focuses on malicious code in site PHP/JS files and can run alongside other tools.

Is a finding proof that a site is compromised?

No. Findings are leads for human review, which is why nothing is quarantined automatically.

Will it be integrated into LionPanel?

Yes, there is a page for LES inside LionPanel.

Tell me when it launches: Lion Exploit Scanner →